FOYSAL×MAHMUD
INITIALIZING… 0%
Identity Check
// CLEARANCE REQUIRED — FILE: FM-1627

All visitors are logged.

SESSION RECORDED · --:--:-- BD
⚠ UNAUTHORIZED REPRODUCTION STRICTLY PROHIBITED ☠ ETHICAL HACKER & DEVELOPER PENETRATION TESTER OSINT SPECIALIST DHAKA · BANGLADESH NDC IT TEAM MEMBER ⚠ UNAUTHORIZED REPRODUCTION STRICTLY PROHIBITED ☠ ETHICAL HACKER & DEVELOPER PENETRATION TESTER OSINT SPECIALIST DHAKA · BANGLADESH NDC IT TEAM MEMBER
Operational — Available for engagement · BD

FOYSAL MAHMUD

"I break into systems — legally — so criminals can't."
▸ETHICAL HACKER

Offensive security with a defensive conscience. I'm hired to think like the adversary — probing web applications, networks and human-facing systems for the weaknesses others miss. Then I help you close them. Properly, permanently, and with evidence.

0+
Yrs in the Field
0+
Clients Secured
0+
Vulnerabilities Found
0+
Projects Shipped
Foysal Mahmud — Ethical Hacker
Foysal MahmudCyber Security Specialist
LAT 23.8103° N
LON 90.4125° E
LOCAL --:--:--
SESSION 00:00:00
THREATCON ACTIVE
ETHICAL HACKER · SECURITY RESEARCHER
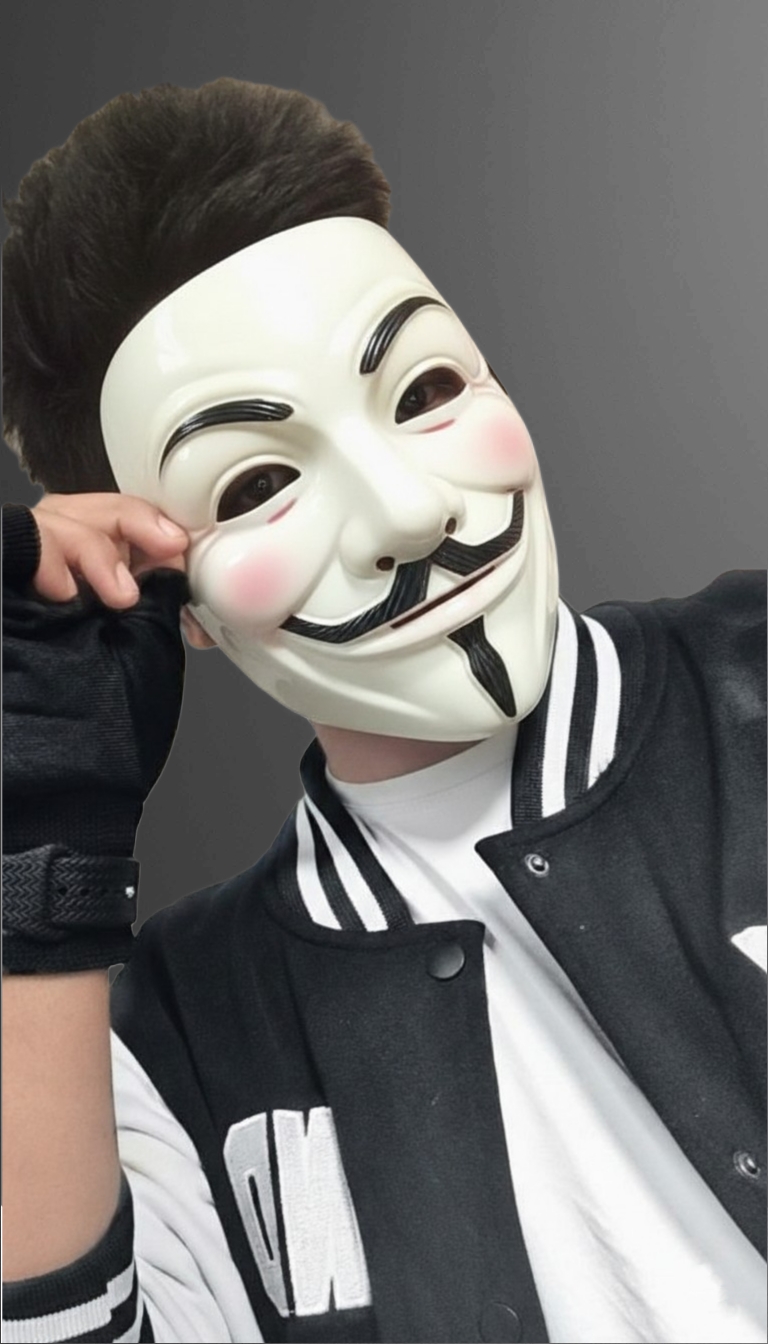
yes, that's really me ↴
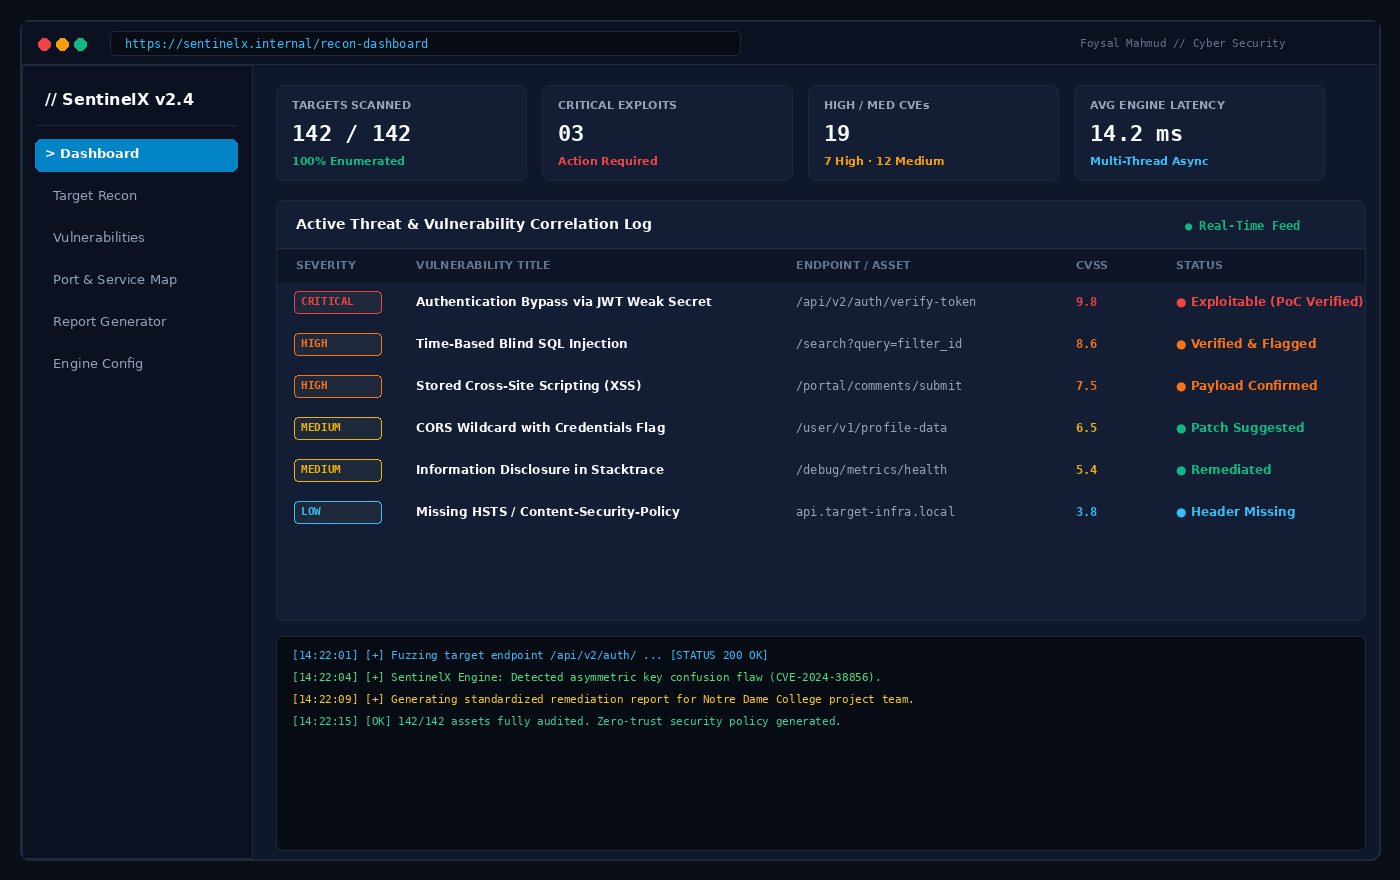
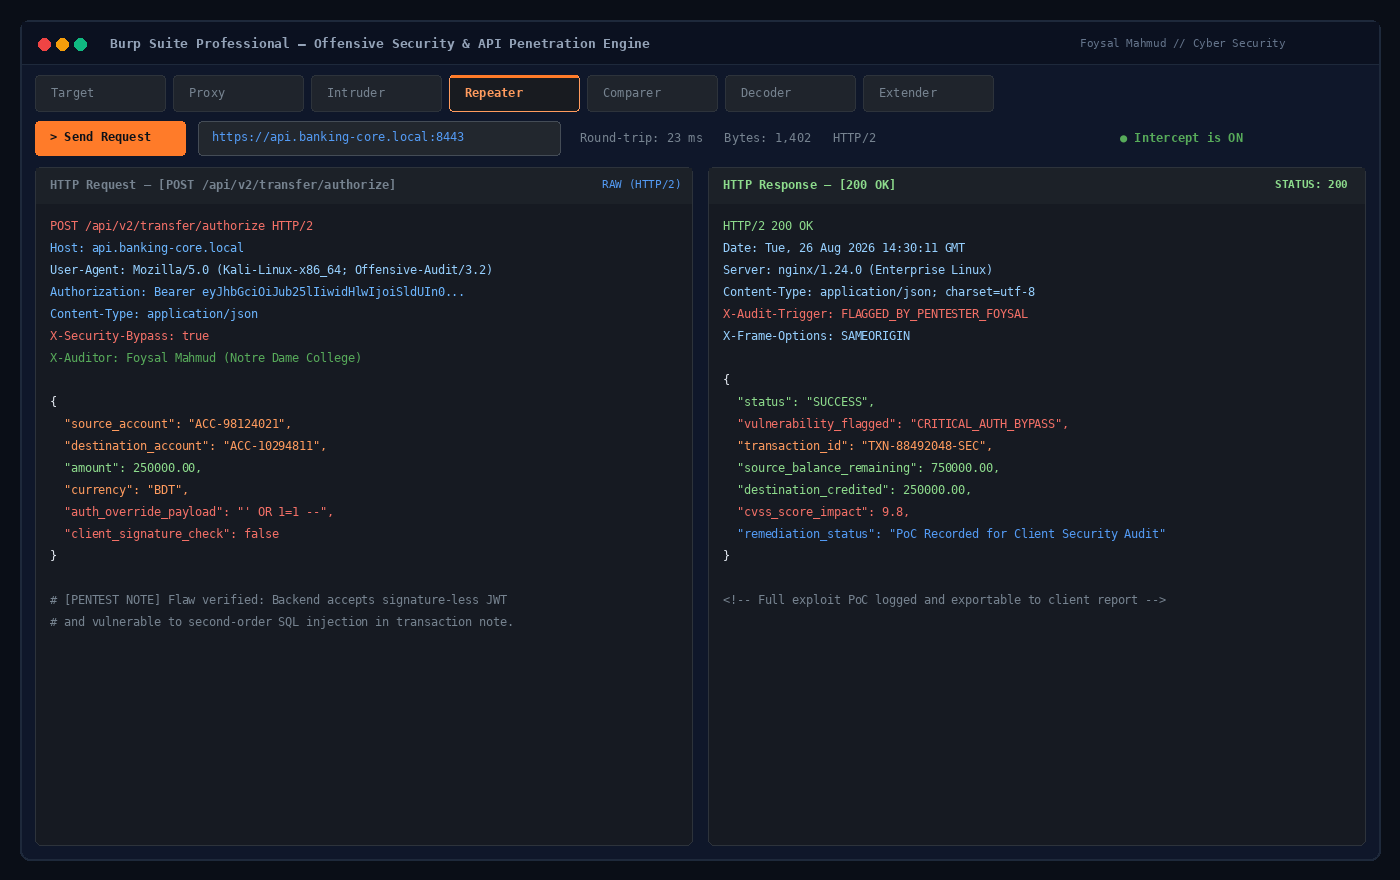
foysal@kali: ~/engagement — AUTO·PLAY
LIVE DEMO
● AUTOMATED — SIT BACK & WATCH recon → audit → report · loops automatically
Scroll
01CONTINUE ▸ FILE 00 — DEPLOYMENTS: ONE DROP & MEAL LEDGER
File 00 // Deployments — 2 live in production
BUILT TO SHIP
not to demo
Two products I designed, built and pushed to production — both handling other people's real data today. Each one has its own case file with the full story, the architecture and a live demo. The short version is right here.
ONE DROP LIVE · LATEST SHIPMENT
№ 121

A volunteer blood-donor network for Bangladesh. A family posts an emergency, the board counts down live, and matching donors surface nearest-first — by blood group, district and distance. Built for the Notre Dame College Batch 27 initiative: student-run, free forever, no sign-up needed to search.

IN PRODUCTION PWA · OFFLINE FIREBASE + FIRESTORE ZERO FRAMEWORK 70 E2E CHECKS
8blood groups matched
25/hrcontact reveal cap
0numbers in the markup
MEAL LEDGER LIVE · V1.3.0
№ 120

A hostel meal-billing engine that cannot lie. Money lives as integer paisa, meals as exact half-units, every hostel rule is encoded in a locked, tested rulebook — and each resident's ledger is isolated server-side by Firestore rules, not by a UI promise.

IN PRODUCTION INTEGER MONEY RULES-ENFORCED ISOLATION ZERO DEPENDENCIES 20 TESTS
৳ EXACTno float drift
20automated tests
~250KBentire PWA
both of them are real products with real users — go ahead, try to break them ↗
02CONTINUE ▸ FILE 01 — THE DOSSIER
File 01 // The Dossier
THE OPERATOR
BEHIND the terminal

Every security career starts with a question. Mine was simple — how do things break? Hi, I'm Foysal Mahmud, a Cyber Security Specialist and Ethical Hacker with 3+ years of hands-on field work. I study at Notre Dame College, Dhaka, and I've chosen to do the unusual: pursue professional offensive security seriously, in parallel with my studies — not as a hobby, but as a craft.

My work spans penetration testing, ethical hacking, OSINT investigations and full-cycle security consulting — for individuals, startups and organizations. I've built and broken enough systems to know exactly where teams usually look away: misconfigurations, trust assumptions, forgotten endpoints and the human layer. Those blind spots are where I operate.

I run every engagement the same way: reconnaissance → exploitation → evidence → remediation. No fear-mongering reports, no jargon walls. You get findings in plain language, proof for every claim, and a prioritized path to fix them. Security is a discipline, not a product — I'm here to be your long-term partner in it.

Notre Dame College Dhaka, BD 3+ Yrs Experience NDC IT Team Open to Work Kali Linux Burp Suite OSINT
// 2021 — GENESIS
First contact with the dark side of the web
Started with a question and a Kali Linux VM. Learned networking, Linux internals and scripting — breaking my own lab machines before touching anyone else's.
// 2022–2023 — THE TURN
From curiosity to methodology
Moved from random CTFs to structured methodology — OWASP, recon workflows, report writing. First paid engagements: web audits for local businesses.
// 2025 — THE INSTITUTION
NDC IT Team & real infrastructure
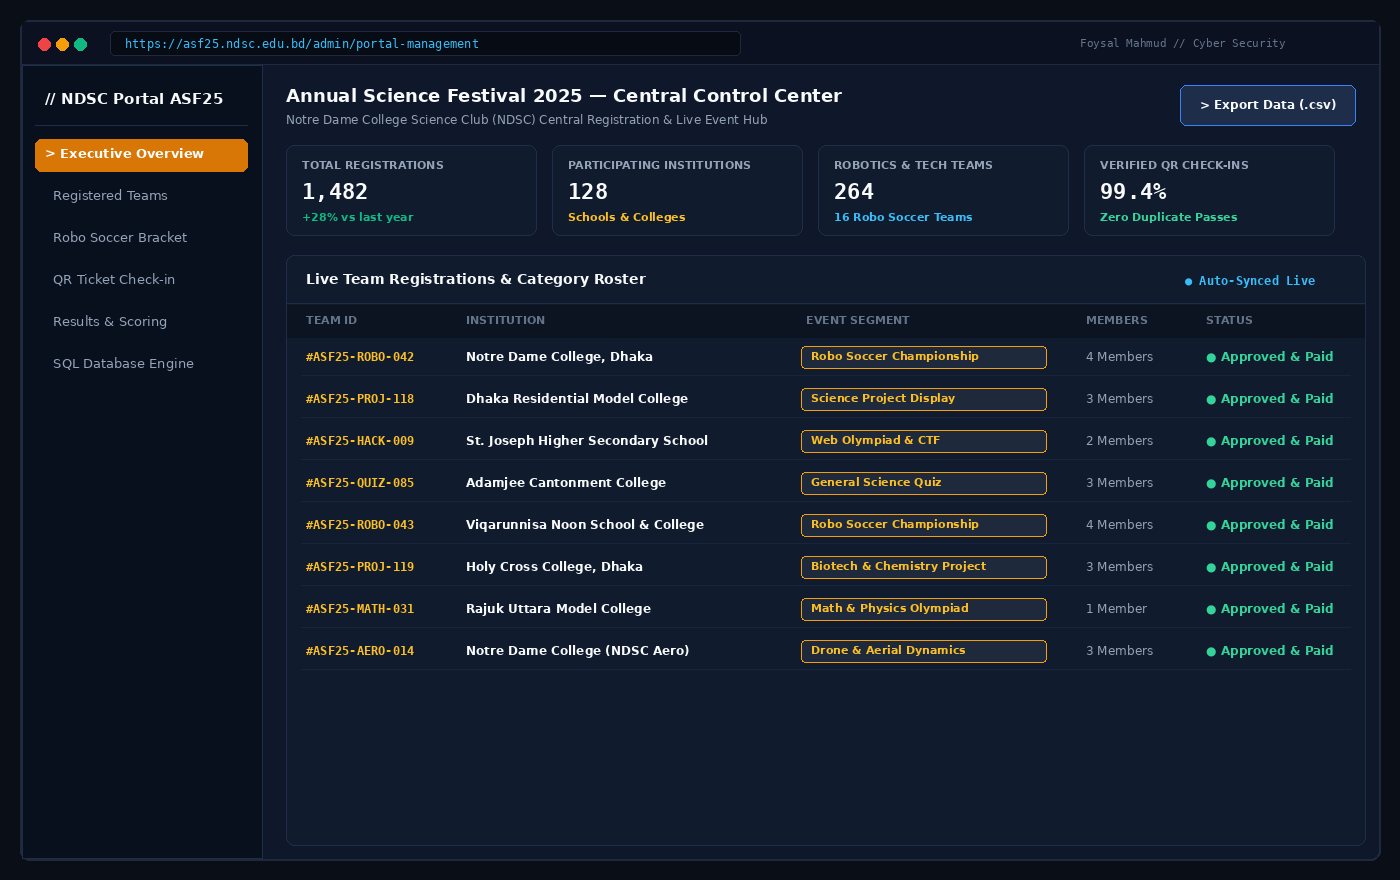
Arrived at Notre Dame College in 2025 — and went straight into the NDC IT Team, building and maintaining official platforms for campus events, including the NDSC Science Festival central hub.
// 2025 — THE STAGE
Shikho Live · AIUB Robotics · public recognition
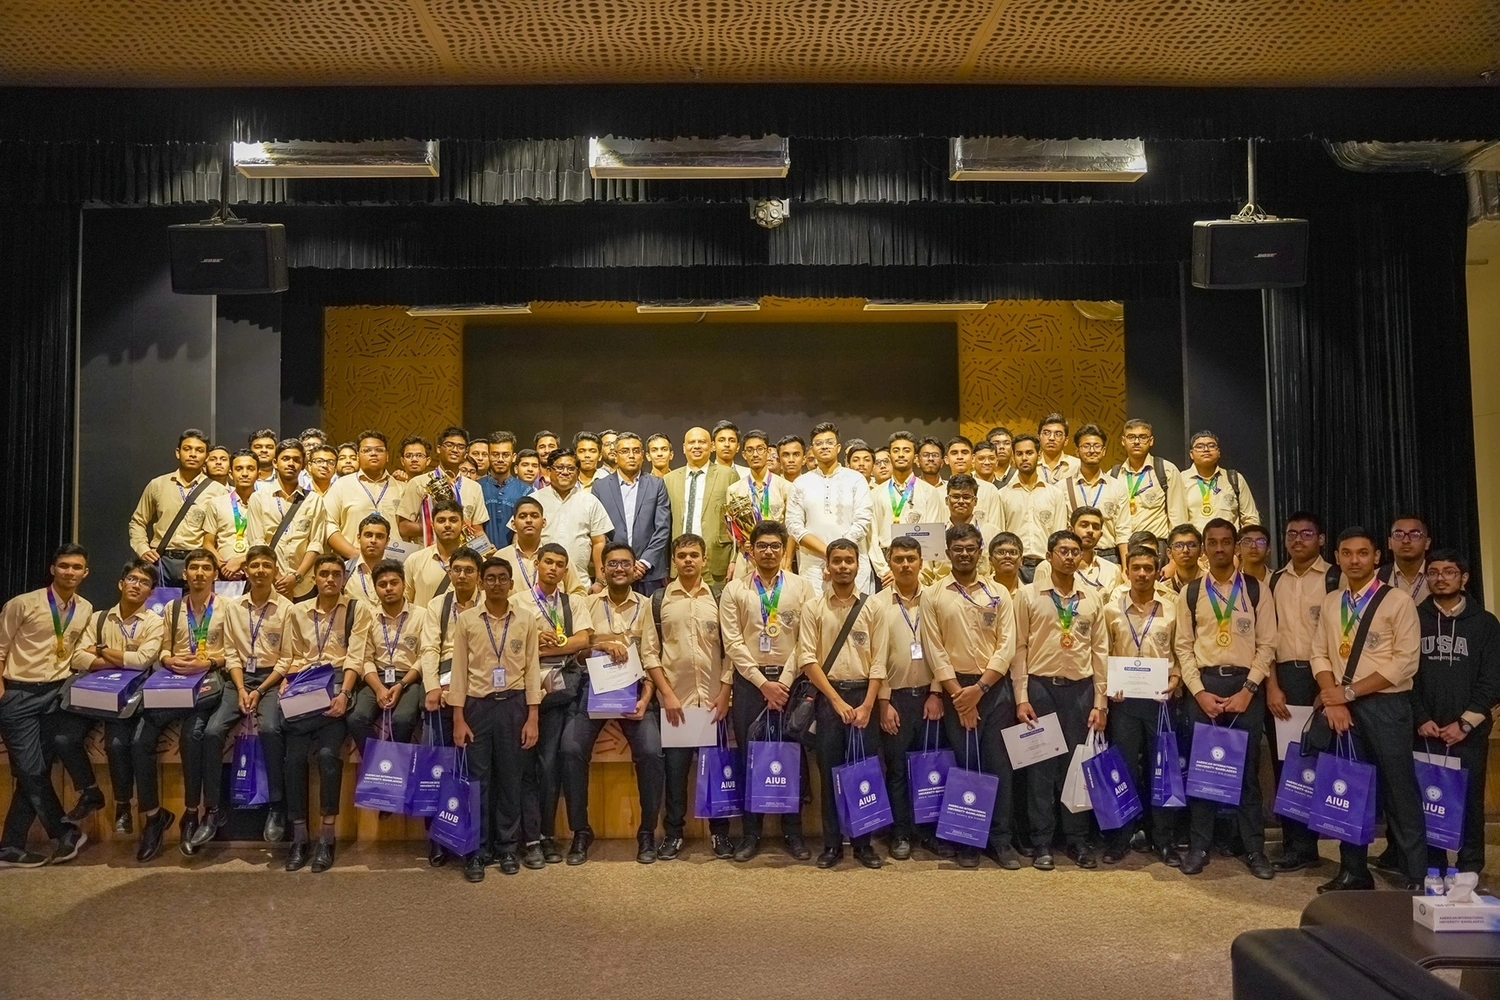
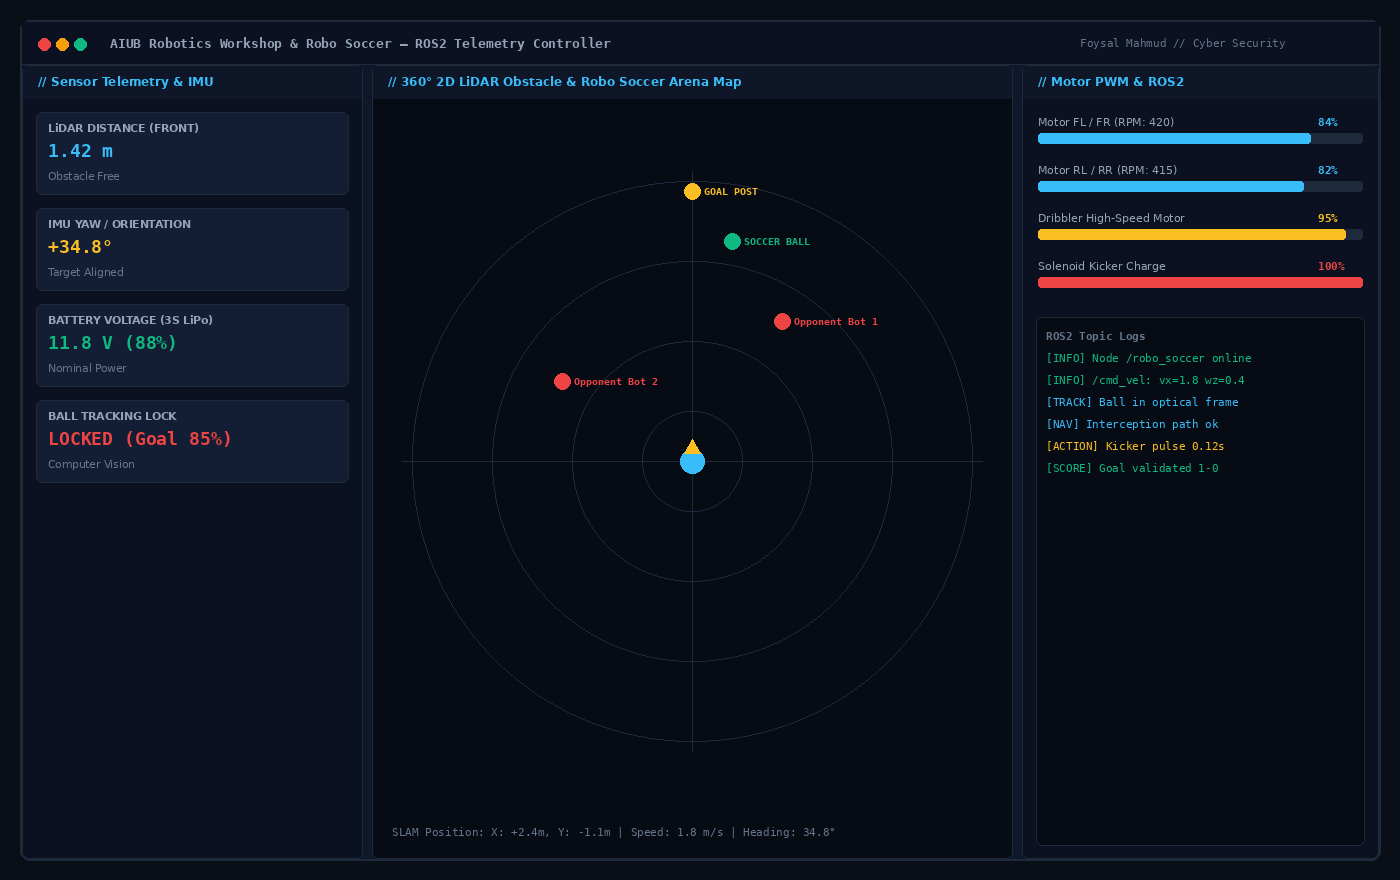
Invited as a Special Guest Merit Student from Notre Dame College on Shikho's 'স্মার্ট স্টার্ট: HSC + AI' live launch — and represented NDSC at the AIUB Robotics Workshop with OSA & AIUB Robotic Crew.
// NOW — THE MISSION
180+ vulnerabilities later
Running engagements for clients worldwide from Dhaka — and still treating every target like it's the one that matters.
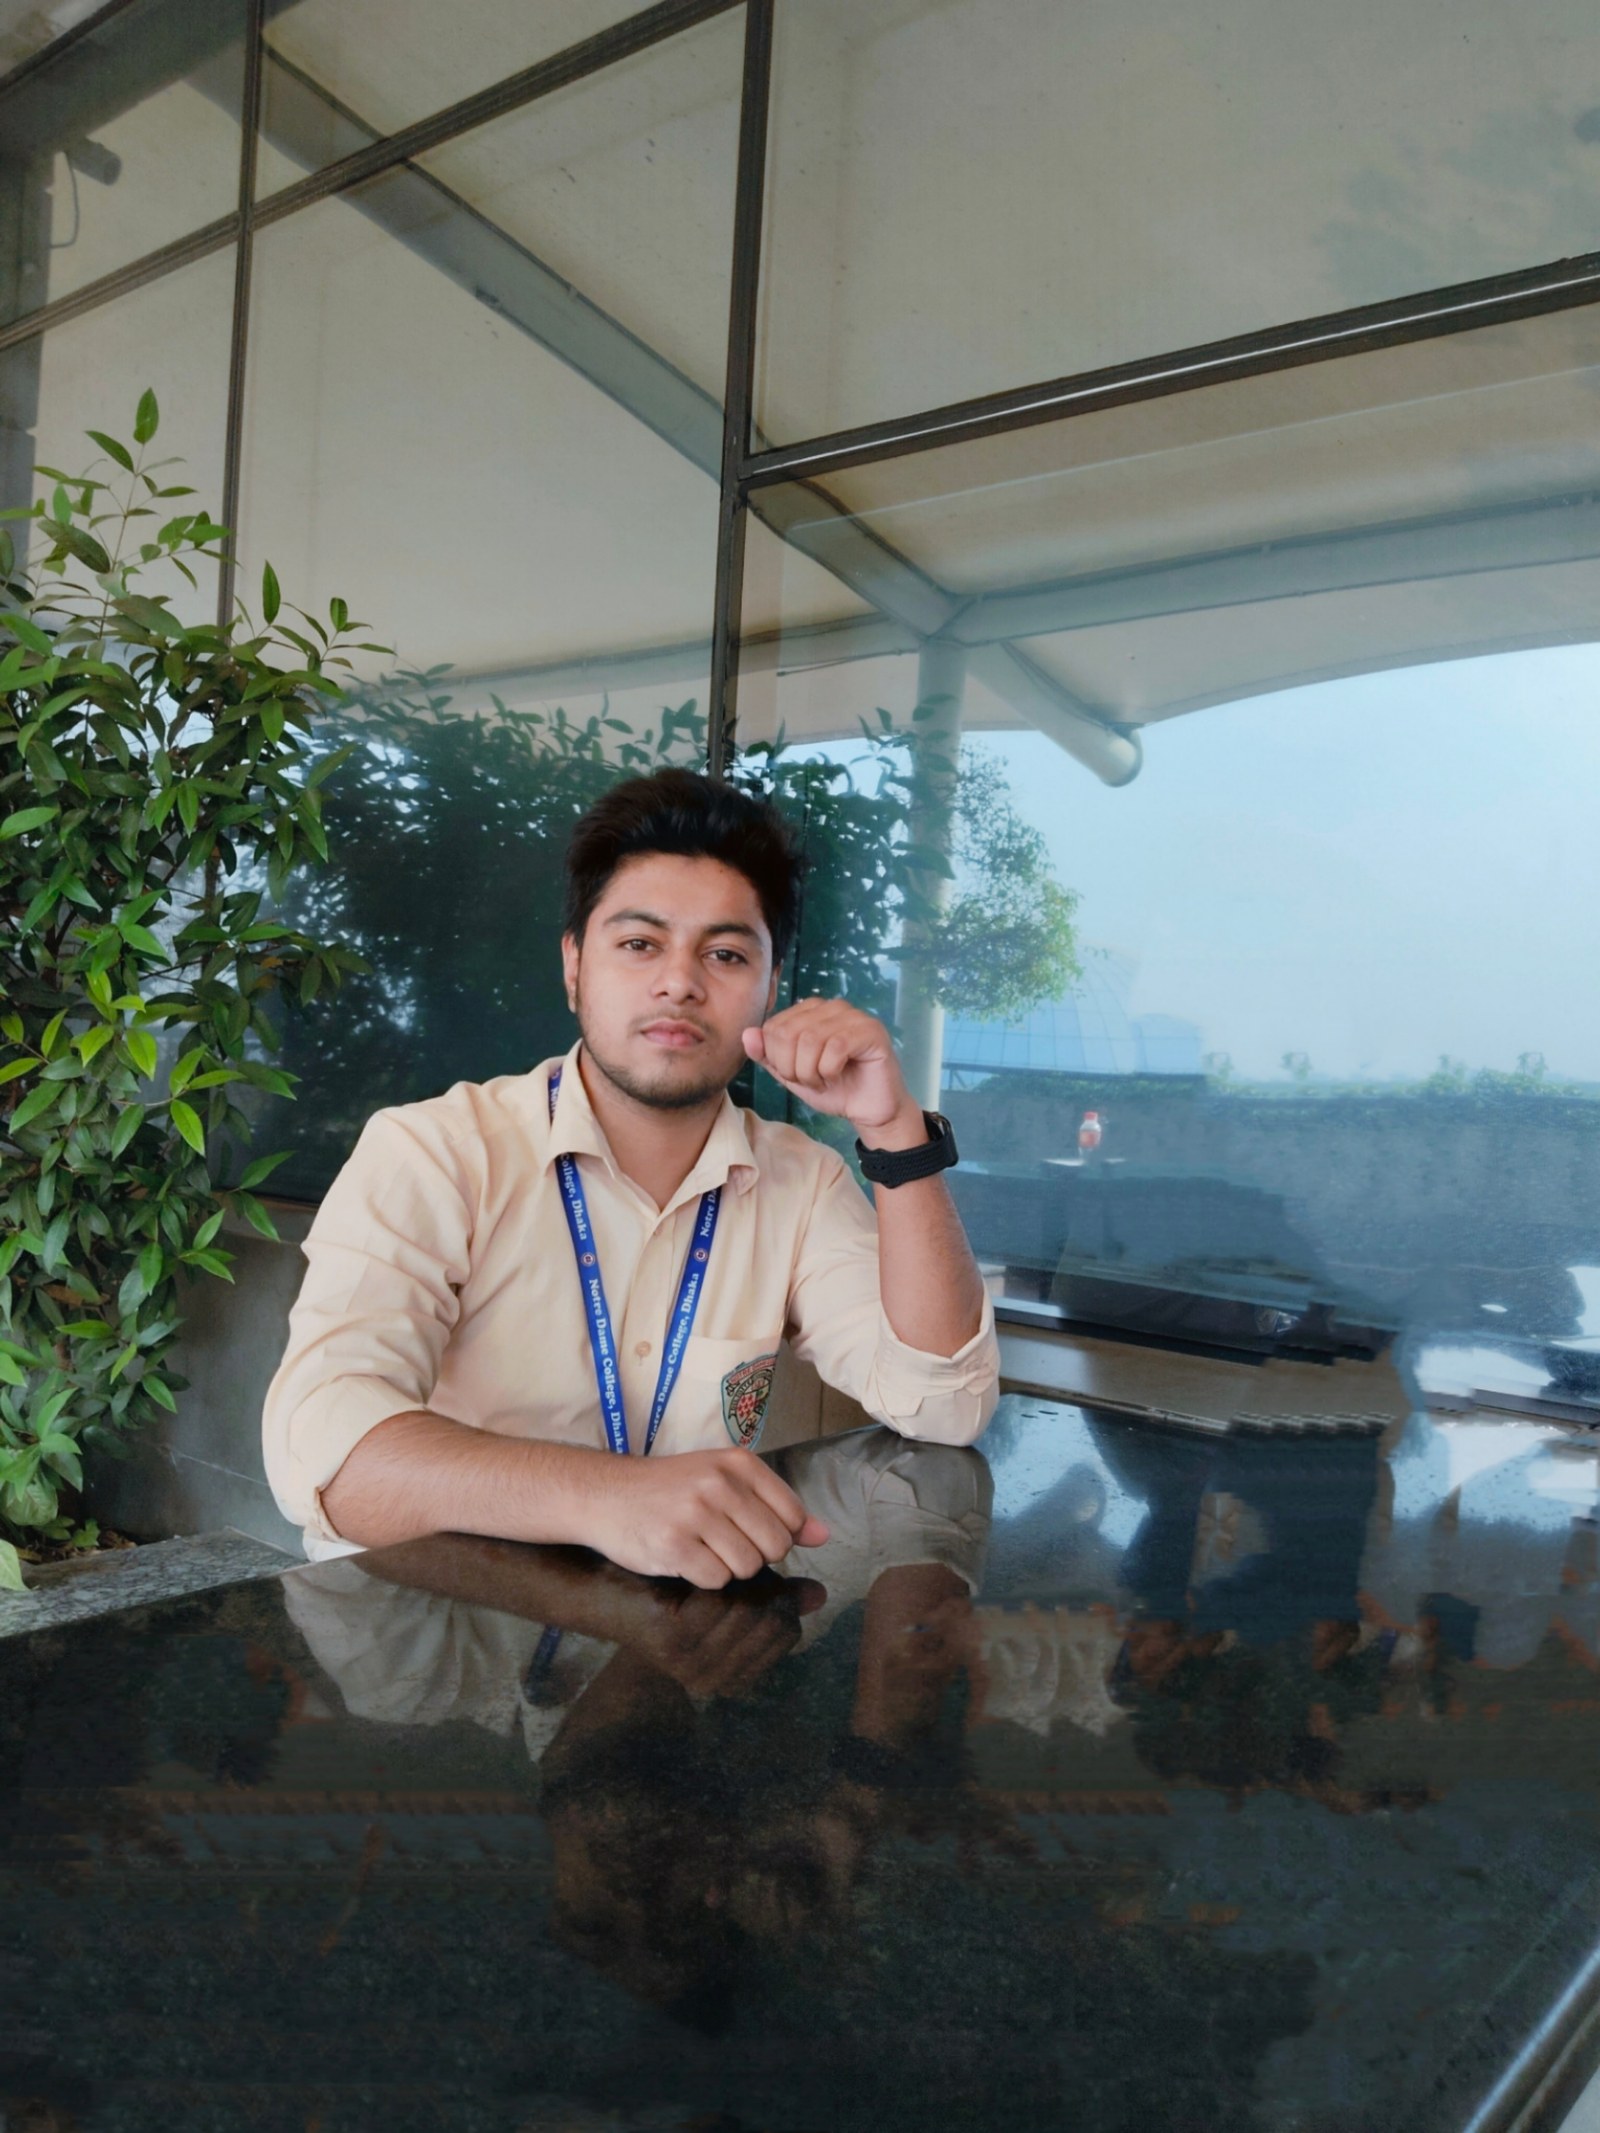
SUBJECT ID // FM-1627 · DHAKA
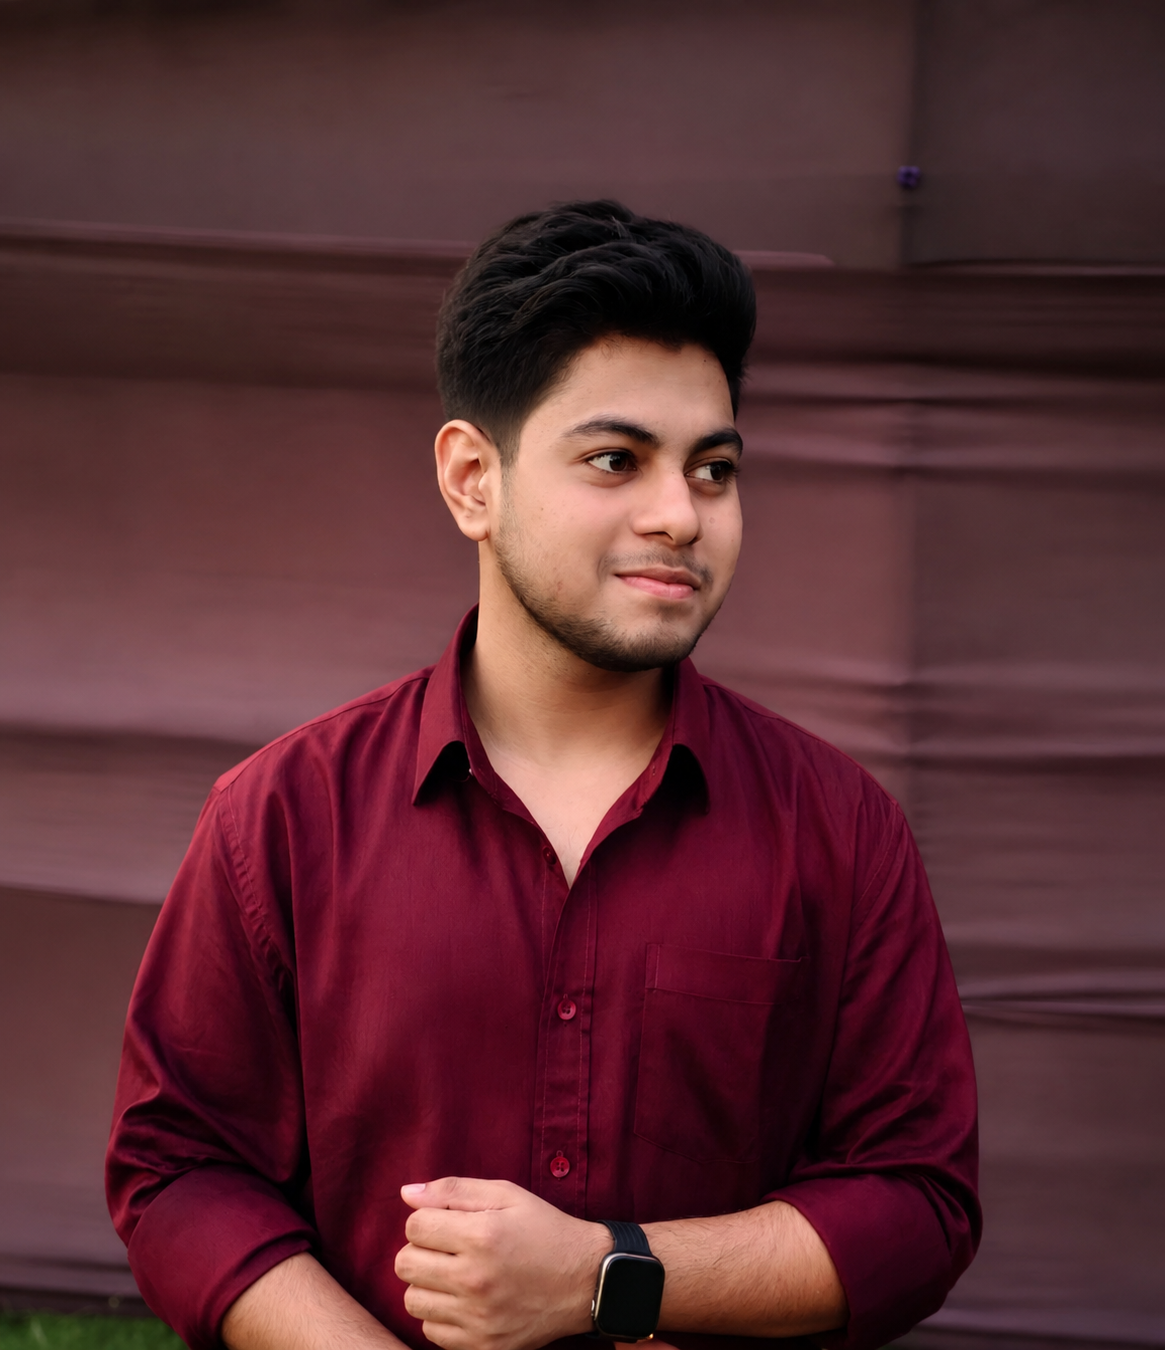
Foysal Mahmud — field photo
somewhere in dhaka — probably debugging something
"The best engagement ends with the client sleeping better — not scared straight. Fear is easy. Confidence takes craft."
— F. MAHMUD · OPERATING PRINCIPLE

P.S. — yes, I really do all of this between classes. Sleep is a scheduled vulnerability.

0
Years in the Field
0
Clients Secured
0
Projects Shipped
0
Vulnerabilities Found
03CONTINUE ▸ FILE 02 — GLOBAL ATTACK SURFACE
File 02 // Live Telemetry
GLOBAL ATTACK
SURFACE monitor

A simulated real-time view of the internet's background noise — port scans, brute-force attempts and intrusion probes hitting monitored infrastructure worldwide. This is the visibility every engagement of mine starts with.

drag it — it's a real 3D globe, not a video ↻
// Target Network — Global Nodes  LIVE
0Packets/s
0Alerts
Risk HIGH
LAT 23.8103°N · LON 90.4125°E · HOME NODE: DHAKA
ORTHOGRAPHIC 3D · WEBGL · REAL-TIME SIM
Drag any direction · double-tap to reset
// 3D RENDERER UNAVAILABLE — LIVE TELEMETRY FEED ONLY
Monitored Node
Active Threat
 Live Intrusion Attempt
// SIMULATION · EDUCATIONAL
0
High-Risk Vulnerabilities · Reported
0
Ports Scanned · Open
0
Critical Exploits · Proven
0
Networks · Assessed
04CONTINUE ▸ FILE 03 — THE ARSENAL
File 03 // Skills & Arsenal
WHAT I KNOW
& HOW I work
CORE COMPETENCIES — SELF-ASSESSED, FIELD-TESTED
Kali Linux / CLI90%
Python Scripting85%
OSINT & Recon82%
Network Pentesting80%
Web App Security78%
JavaScript / HTML / CSS72%
Tools don't make a hacker — methodology does. The arsenal below just makes the methodology faster.
Burp Suite
Metasploit
Nmap
Wireshark
SQLMap
Nikto
Git / GitHub
Linux Admin
Social Engineering
OSINT Stack
yes, my lab wifi is named "FBI Surveillance Van #4"
05CONTINUE ▸ FILE 04 — CAPABILITIES
File 04 // Capabilities
WHAT I BRING
TO your table

Five disciplines, one mindset: assume nothing, verify everything, and leave the system harder than you found it.

// Service 01
ETHICAL
HACKING

Authorized, simulated attacks against your systems — executed exactly like a real adversary would. I probe your infrastructure for the weaknesses an attacker would find first, then hand you a risk-rated report with proof-of-concept evidence and a remediation roadmap — before someone with worse intentions finds the same doors.

Start an Engagement
01
most requested ★ Ethical Hacking
// Service 02
PENETRATION
TESTING

Deep-dive security assessments where automation meets craft. Scanners find the obvious; I hunt the logic flaws, chained misconfigurations and business-logic abuses that tools can't reason about. Web apps, APIs, networks and mobile — every finding delivered with PoC evidence and business-impact analysis.

Start an Engagement
02
Penetration Testing
// Service 03
SECURITY
CONSULTING

Strategy before tooling. Threat modeling, risk assessment, incident-response planning and security culture — tailored to your risk landscape and budget, not a generic checklist. Whether you're a startup shipping your first product or an organization hardening what already exists, I help build a posture that lasts.

Start an Engagement
03
Security Consulting
// Service 04
SECURE
DEVELOPMENT

I don't just find vulnerabilities — I know how they get written. Landing pages, platforms and web applications built secure by design: validated inputs, hardened headers, sane auth, clean architecture. The rare developer who has read your codebase from the attacker's side first.

Start an Engagement
04
Secure Web Development
// Service 05
OSINT &
RECON

What does the internet already know about you? Open-source intelligence gathering and digital-footprint analysis that shows exactly what an attacker learns before they ever knock on your firewall — exposed records, leaked credentials, metadata trails — and how to shrink that footprint.

Start an Engagement
05
OSINT & Recon
06CONTINUE ▸ FILE 05 — ENGAGEMENT PROTOCOL
File 05 // Engagement Protocol
HOW AN ENGAGEMENT
actually runs

No mystery, no black box. Every engagement follows the same four-phase protocol — you know what's happening at every step, and you get full documentation when it's done.

01
Recon & Scoping
We define targets, rules of engagement and success criteria. A signed scope-of-work protects both sides. Then passive reconnaissance: mapping your attack surface the way an adversary would — before touching anything.
DELIVERABLE: SCOPE DOCUMENT
02
Exploitation & Proof
Controlled attacks against the agreed scope — automated tooling for coverage, manual work for depth. Every vulnerability is verified and exploited only far enough to prove real impact. No damage, no drama, full evidence.
DELIVERABLE: PoC EVIDENCE LOG
03
Reporting & Debrief
A professional report in plain language: findings ranked by real business risk, reproduction steps, screenshots, and a live debrief call where I walk your team through every issue — and answer everything.
DELIVERABLE: FULL PDF REPORT
04
Remediation & Harden
A prioritized fix plan your developers can actually execute. I stay available through implementation, re-test the fixes, and verify the attack surface is genuinely smaller — not just declared fixed.
DELIVERABLE: RE-TEST & SIGN-OFF
07CONTINUE ▸ FILE 06 — FIELD RECORDS
File 06 // Field Records
SELECTED OPERATIONS
from the field

A sample of real engagements — anonymized and redacted to protect client confidentiality. Hover the redactions to decrypt. Full references available on request.

↓ real cases — names hidden for obvious reasons
REC-0117 DECLASSIFIED
OP · NIGHTFALL
CLIENT: E-COMMERCE PLATFORM, DHAKA
WEB APPPRE-LAUNCH72H WINDOW
  • SQL injection — customer database exposedCRITICAL
  • Broken access control on admin panelHIGH
  • Payment callback forgery possibleHIGH
  • Verbose error leakage on 3 endpointsMEDIUM
OUTCOME: PATCHED BEFORE LAUNCH 2024
REC-0203 DECLASSIFIED
OP · GLASSHOUSE
CLIENT: FINTECH STARTUP, SINGAPORE
APIOSINTREMOTE
  • IDOR — transaction records of any userCRITICAL
  • JWT signature not validatedCRITICAL
  • Employee credentials found in leaksHIGH
  • Rate limiting absent on OTP endpointMEDIUM
OUTCOME: SECURITY OVERHAUL DELIVERED 2025
REC-0289 DECLASSIFIED
OP · PAPER TRAIL
CLIENT: EDUCATIONAL INSTITUTION, BD
NETWORKINTERNALON-SITE
  • Default creds on 4 network devicesCRITICAL
  • Student records system exposed to LANHIGH
  • Rogue Wi-Fi hotspot impersonating staff netHIGH
  • No logging on perimeter firewallMEDIUM
OUTCOME: HARDENED + STAFF TRAINED 2025
OPERATION NAMES ARE RANDOMLY ASSIGNED · CLIENT IDENTITIES PROTECTED UNDER NDA · DETAILS PUBLISHED WITH PERMISSION
08CONTINUE ▸ FILE 07 — PUBLIC RECORD
File 07 // Public Record
KEYNOTE & achievements

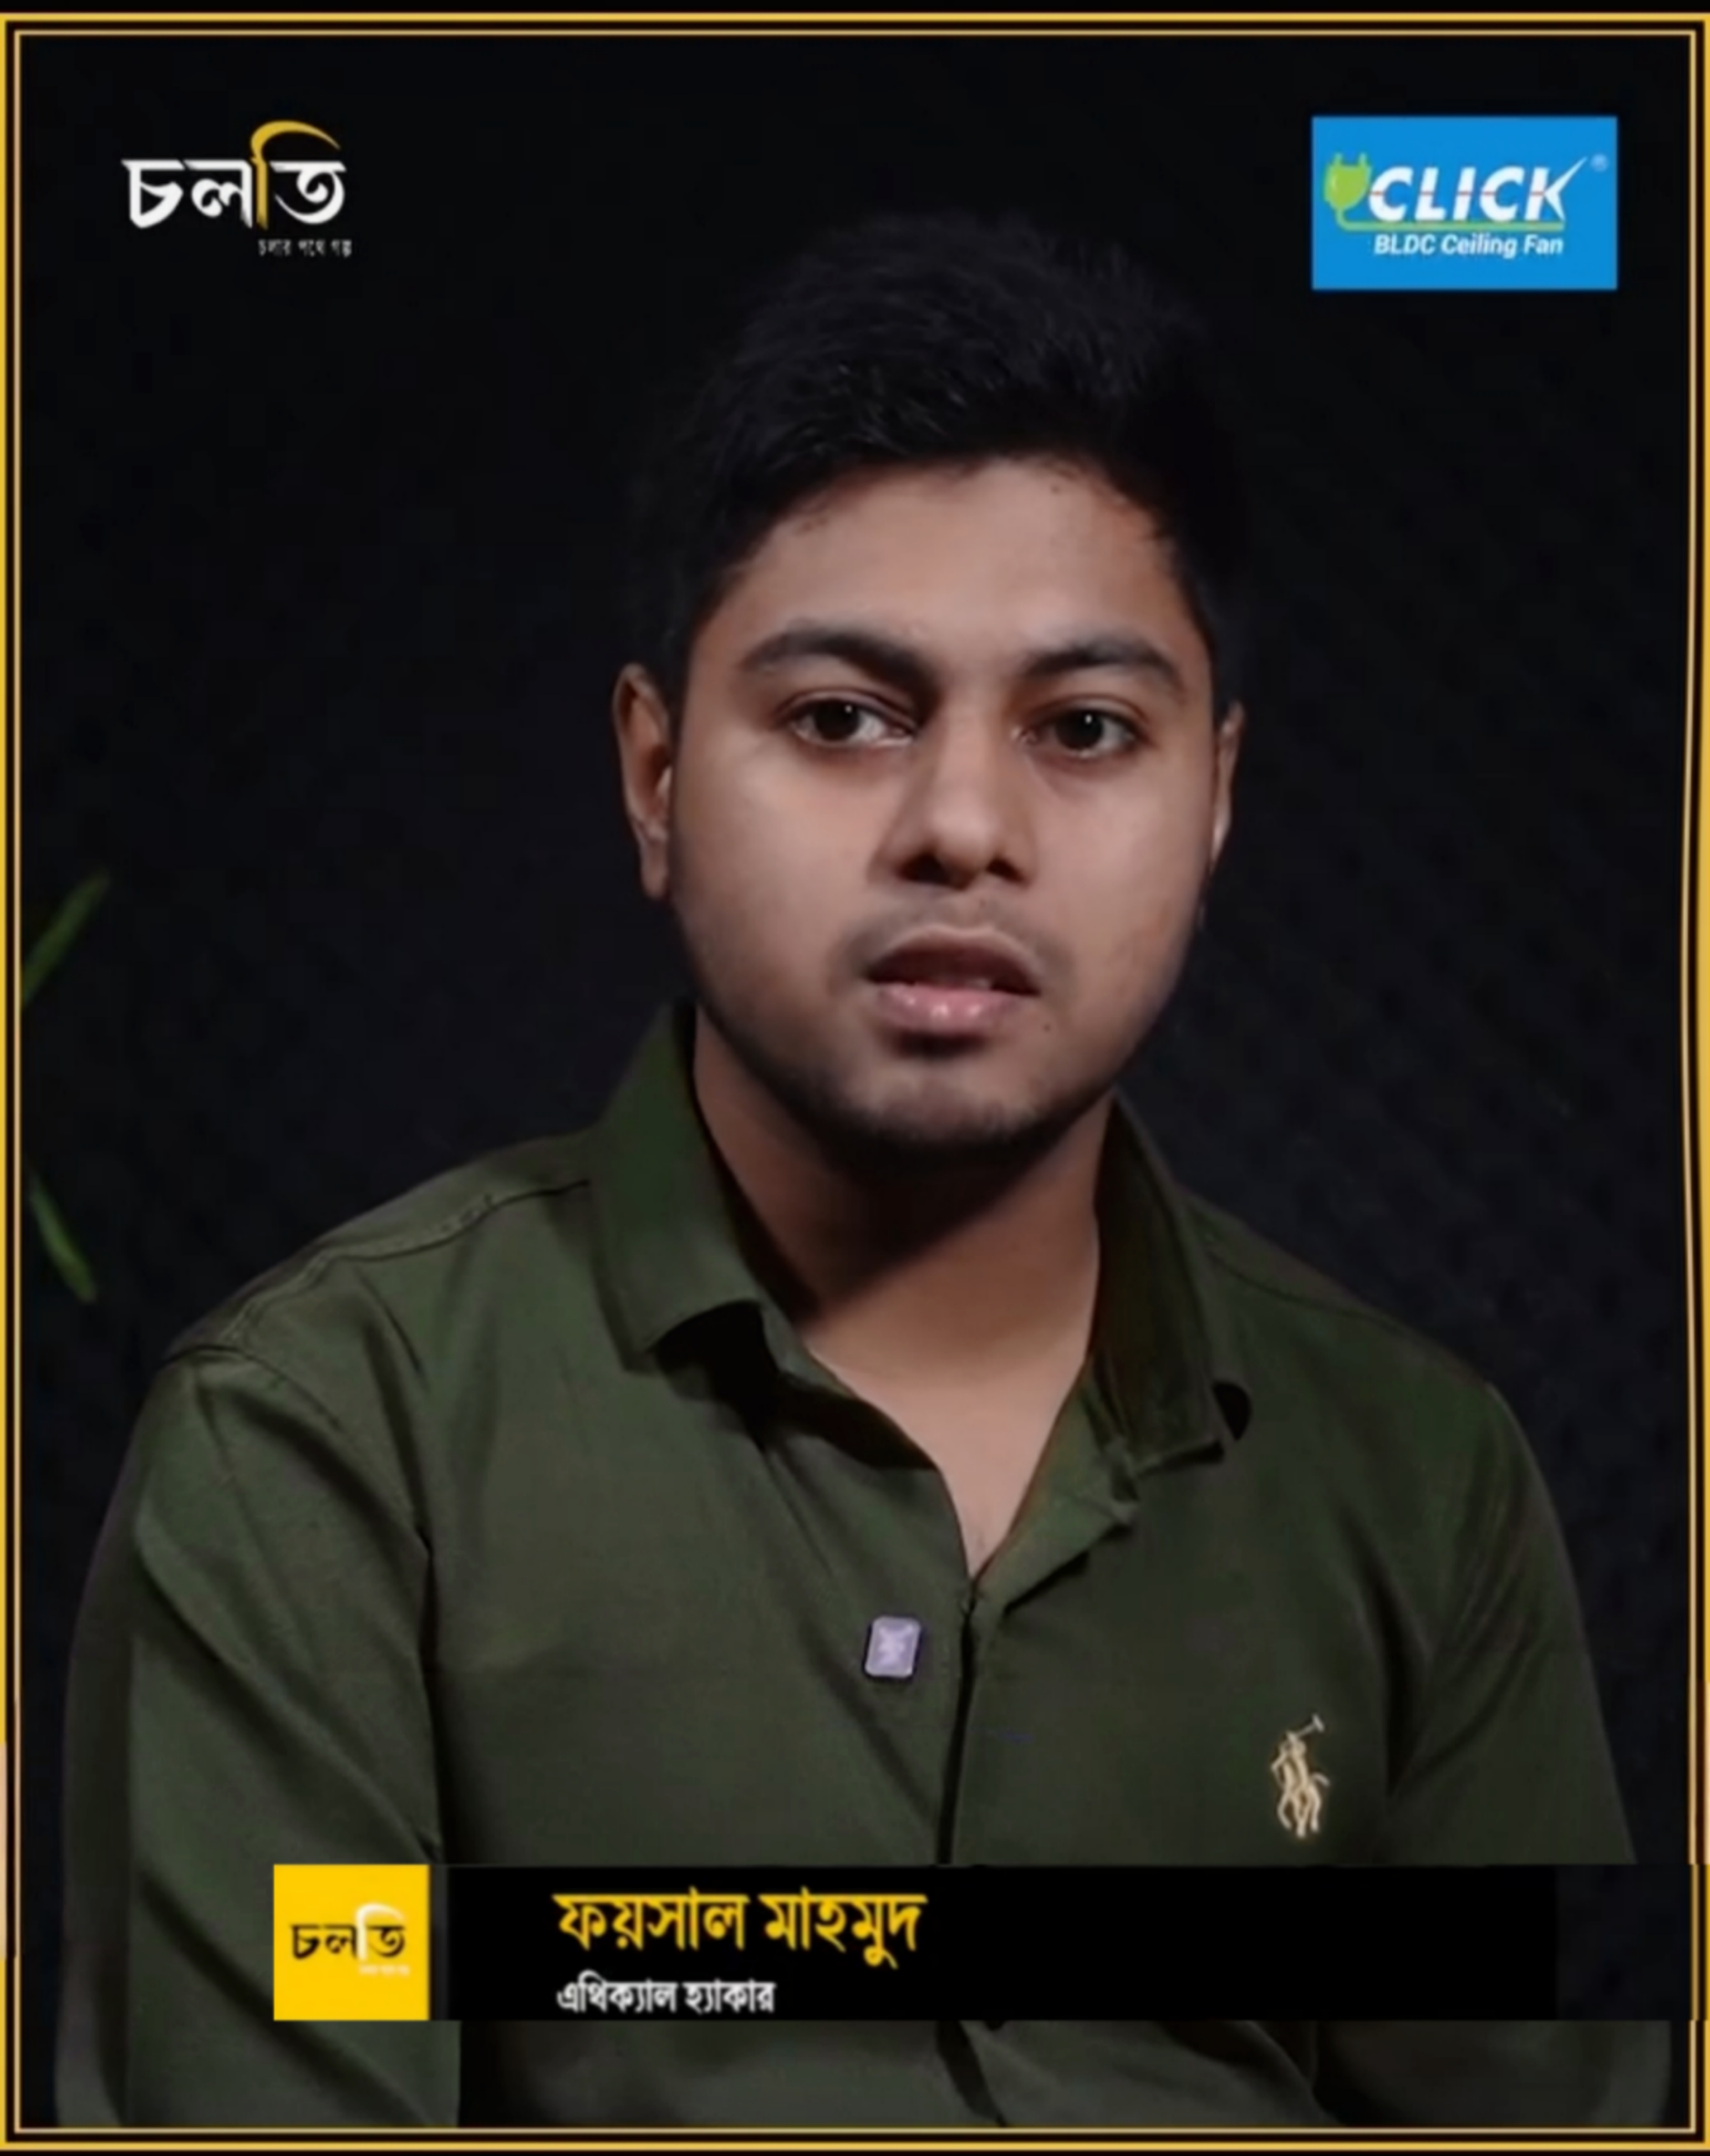
Security is the craft — but the field is wider than the terminal. From an ethical-hacking interview with চলতি and guest-speaking on national ed-tech live streams, to representing Notre Dame College in robotics outreach at AIUB and building the digital backbone for institutional science events.

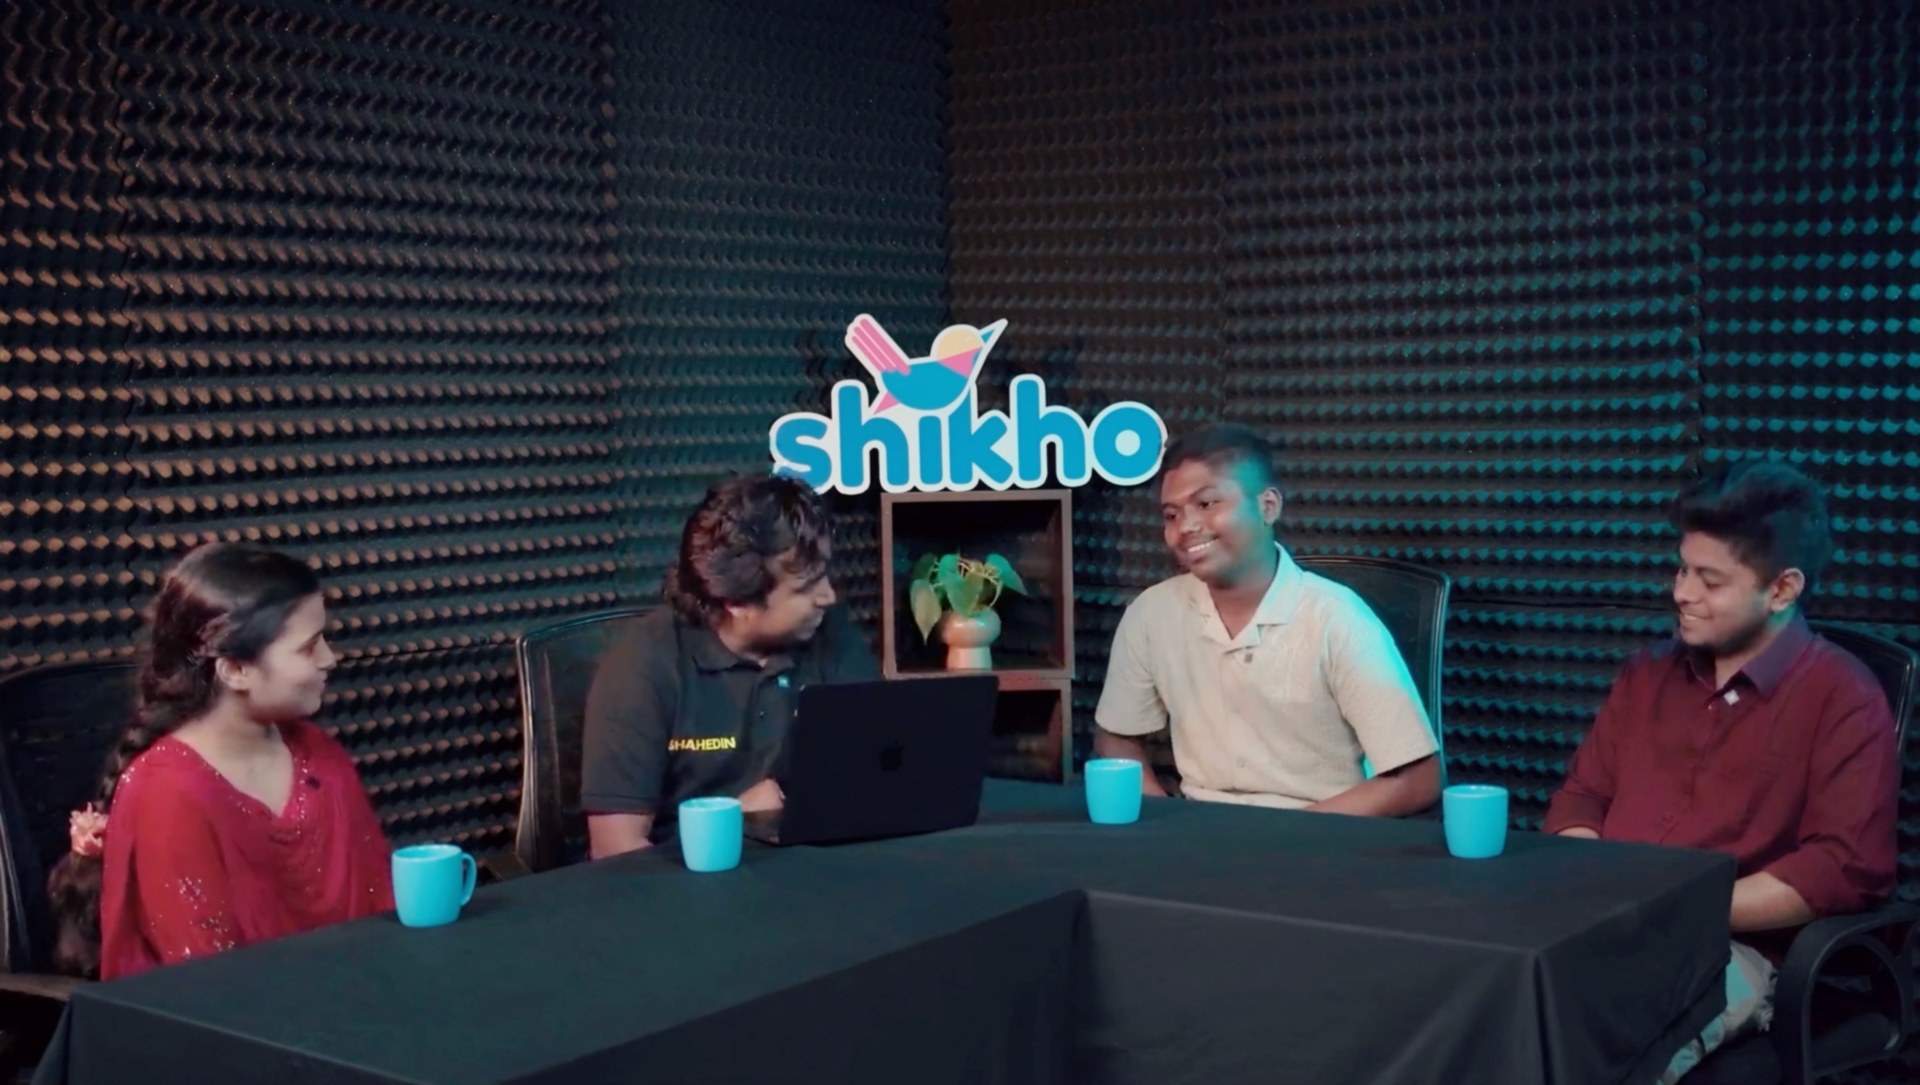
// SHIKHO SPECIAL GUEST Foysal Mahmud at Shikho HSC + AI Live
'স্মার্ট স্টার্ট: HSC + AI' LIVE LAUNCH

Special Guest on Shikho Live, with Shahedin

Invited as a Special Guest Merit Student from Notre Dame College for Shikho's flagship live launch — speaking on the SSC→HSC transition, how AI belongs in a smart study system, and practical roadmaps for incoming HSC batches.

// AIUB ROBOTICS WORKSHOP Workshop on Robotics for NDSC at AIUB
22 NOV 2025 · AIUB CAMPUS

Robotics Workshop for NDSC, hosted at AIUB

With OSA & the AIUB Robotic Crew (ARC), bringing 66 Notre Dame College Science Club students into the lab: 3D CAD modeling, live drone demos, a Robo Soccer championship — and trophies and medals that traveled back to NDC with the team.

// NDC LEADERSHIP Notre Dame College IT Team & NDSC
NOTRE DAME COLLEGE, DHAKA

NDC IT Team & NDSC — Builder Duty

Active developer and technician for the Notre Dame College IT Team and NDSC — designing and running the official platforms behind the Annual Science Festival and campus tech initiatives. The invisible systems behind visible events.

09CONTINUE ▸ FILE 09 — INTERCEPTED SIGNALS
File 09 // Intercepts
SIGNALS FROM clients
Verified
"
★★★★★

Foysal did an outstanding job on our web application security audit. He found critical vulnerabilities our internal team had completely missed — including an SQL injection that could have exposed our entire user database. The report alone was worth the engagement.

Rafiqul Islam
Verified
"
★★★★★

Professional, fast, and extremely knowledgeable. Foysal stress-tested our e-commerce platform before launch and found 3 critical and 7 medium-risk issues. The penetration test report was detailed, clear, and very actionable — our devs fixed everything in one sprint.

Sakib Hossain
Verified
"
★★★★★

Working with Foysal was great from start to finish. He explained every finding in plain language, provided PoC screenshots, and gave a clear remediation roadmap. Will definitely work again.

Nusrat Jahan
Verified
"
★★★★★

Hired Foysal for an OSINT investigation and network security review. He delivered a well-organized report within the timeline. Communication was excellent and the quality of work exceeded expectations.

Arif Chowdhury
10CONTINUE ▸ FILE 10 — CLEARANCE QUESTIONS
File 10 // FAQ
CLEARANCE questions
What services do you offer?
Ethical hacking, web application penetration testing, network security assessments, OSINT investigations, vulnerability scanning, and ongoing cybersecurity consulting. One-time audit or long-term partnership — both start with a conversation.
How do I get started?
Reach out via WhatsApp, Facebook, or email. I respond within 24 hours to discuss requirements, define scope, and provide a quote. Every engagement starts with a free initial consultation — no strings attached.
Is ethical hacking actually legal?
100% — when performed with explicit written authorization. I require a signed scope-of-work agreement before touching any system, and all work is fully compliant with applicable laws. No authorization, no engagement. That line never blurs.
How long does an engagement take?
A focused web application audit typically takes 3–5 days. A full network penetration test runs 1–2 weeks. OSINT investigations: 2–4 days. You get a precise timeline before we begin — no surprises, no scope creep.
What does the final report include?
A professional PDF document: every vulnerability with risk rating (Critical / High / Medium / Low), proof-of-concept evidence, business impact analysis, and step-by-step remediation guidance — plus a live debrief call where I walk your team through it.
What is your pricing?
Pricing scales with scope and complexity — with competitive rates for individuals, startups, and enterprises. Contact me for a free quote: transparent pricing, no hidden charges, no surprises on the invoice.
11CONTINUE ▸ FINAL FILE — OPEN A CHANNEL
Final File // Contact
OPEN A SECURE
channel
Ready when
you are.
my AI assistant replies fast — usually faster than this page loads

Whether it's a full penetration test, a second opinion on your security posture, or a question you'd rather ask privately — reach out. First consultation is free, and everything you share stays confidential.

Dhaka, Bangladesh · Operating Worldwide (Remote)
Response < 24h NDA Friendly Confidential by Default
Foysal Mahmud — contact
Transmit a Message
// Response within 24 hours — encrypted & private
— Select a topic —
Penetration Testing
Web App Security Audit
Network Security
OSINT Investigation
Vulnerability Assessment
Consulting / Advisory
Other
— Optional —
Under $100
$100 – $500
$500 – $2,000
$2,000+
Let's discuss
Transmission received. I'll get back to you within 24 hours.
Something went wrong. Please try again or contact directly via email.

Welcome to the Secret Vault 🔐

You have successfully accessed the private area. This page is only visible to verified clients. Here you can find exclusive resources, advanced cybersecurity tips, and direct contact protocols.

Foysal's AI
Online
 Encrypted Session
Hey! I'm Foysal's AI assistant. Ask me anything about cybersecurity, services, or how to get in touch. 🔐
About Foysal? Services? How to hire? Contact info? Blogs? Foysal's photo?
Projects — One Drop & Meal LedgerP
Case File № 121 — One DropO
Case File № 120 — Meal LedgerM
Open Dossier — About1
Live Threat Map2
Skills & Arsenal3
Capabilities — Services4
Field Records — Case Files5
Engagement Protocol6
Visual ArchiveG
Contact — Hire MeH
Open Secret VaultS
Open AI AssistantA
Automated Terminal — Watch the DemoT
চলতি Interview — Full Case StudyC
?? — Overdrive~