Portfolio/File 07 — Public Record/ চলতি Interview
Featured Interview 23 September 2026 3 Videos · YouTube & Facebook

Ethical Hacking,
Explained on চলতি

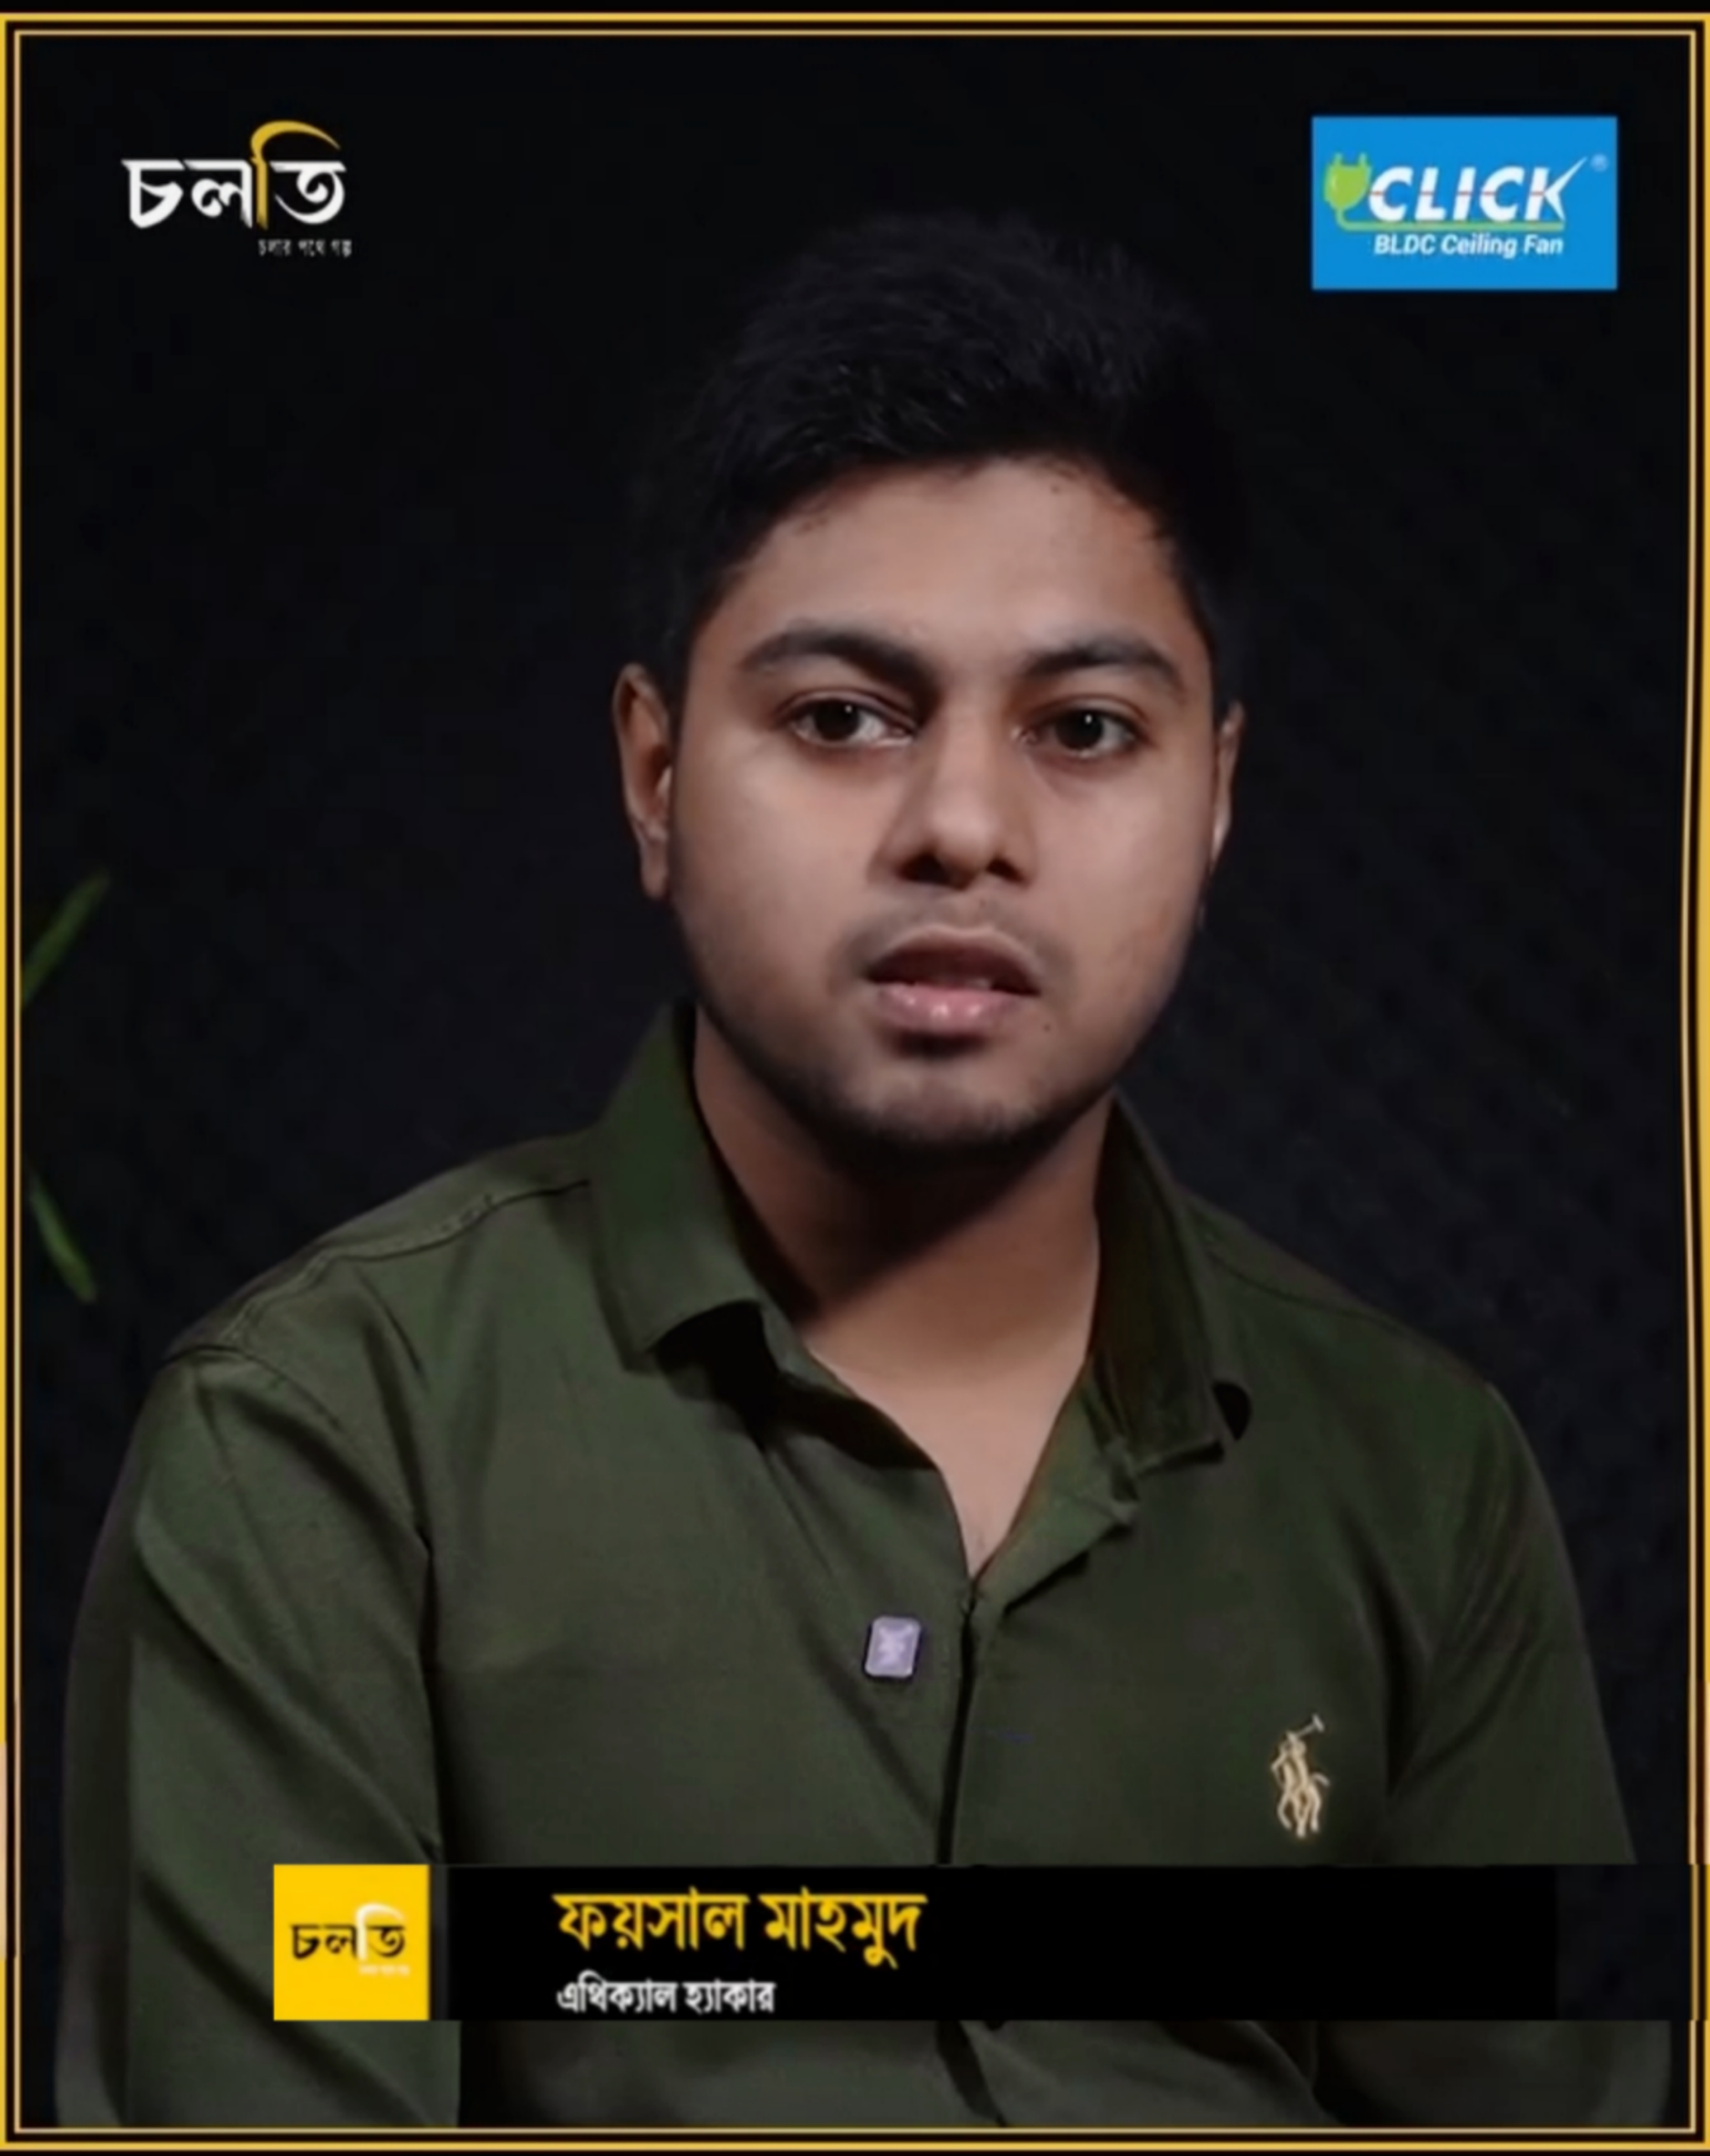
Foysal Mahmud — Ethical Hacker — sat down with চলতি for a dedicated interview session on Ethical Hacking & Cybersecurity: what authorized hacking actually looks like, how real attacks unfold, and what ordinary people and businesses can do today to stay safe. This page is the complete case study of that session.

Guest
Foysal MahmudEthical Hacker · Dhaka, Bangladesh
Host / Platform
চলতিInterview Session · YouTube & Facebook
Date
23 Sep 2026Wednesday · Video Series
Topic
Ethical Hacking& Cybersecurity Awareness
Foysal Mahmud — Ethical Hacking and Cybersecurity interview with চলতি
Figure 01 · চলতি Interview SessionEthical Hacking & Cybersecurity · 2026
01 // The Session

Why this conversation mattered

Most people only meet the word “hacker” in headlines — after a breach, a stolen account, or money gone from a mobile wallet. The work that prevents those headlines is almost invisible. This session with চলতি put that invisible work in front of a general audience: what an ethical hacker is hired to do, where the legal line sits, and why the same techniques that protect a system in authorized hands become a crime without permission.

For Foysal Mahmud, the interview was also a chance to translate a technical craft into plain language — recon, vulnerabilities and reports became stories about trust, evidence and responsibility. Security awareness only works when non-technical people can act on it, and that translation is the point of sessions like this.

“I break into systems — legally — so criminals can't.”

— Foysal Mahmud · operating principle, discussed in the session
02 // Inside the Interview

What was discussed

Six themes structured the conversation — from the definition of the craft to a checklist any viewer could apply the same evening.

THEME · 01

The line between an expert and a criminal

Authorization is everything. An ethical hacker works under a signed scope — what may be tested, what is off-limits, and how findings are handled. The same action without permission is simply a crime, whatever the intention claimed afterwards.

THEME · 02

How real attacks actually happen

Real intrusions rarely look like movies. Attackers start with public information — exposed accounts, forgotten subdomains, leaked credentials — then chain small weaknesses together. Recon first, spectacle never.

THEME · 03

The human layer is the softest target

Phishing pages, fake support calls and “urgent” messages compromise more accounts than exotic exploits. Password reuse turns one old leak into every account a person owns — which is why habits, not just tools, decide safety.

THEME · 04

What businesses consistently get wrong

Launching first and securing later, staging servers left public, admin panels protected by hope. The session walked through why a pre-launch audit is cheaper — in money and reputation — than a post-breach apology.

THEME · 05

What an engagement actually delivers

Not a scare, a system: risk-rated findings with proof, a remediation roadmap, and a re-test after fixes. The report is the product — evidence a team can act on, in the order that matters most.

THEME · 06

Starting out in cybersecurity

For students watching: Linux, networking fundamentals and one scripting language before any “hacking tool”. Methodology outlasts tools — and documented, authorized practice is how a portfolio gets built.

03 // Key Takeaways

If you remember five things

  1. Permission is the profession. Ethical hacking is defined by authorization and scope — technique is secondary.
  2. Attackers do homework first. Most of an intrusion is public-information gathering; shrinking your digital footprint is real defense.
  3. One reused password is every password. A unique password per account, in a manager, with two-factor authentication on, stops the most common attack outright.
  4. Security is cheapest before launch. An audit costs a fraction of a breach — and findings arrive while they are still easy to fix.
  5. Awareness is a skill anyone can train. Slow down on urgent messages, verify through a second channel, and treat unexpected links as hostile until proven otherwise.
04 // Viewer Checklist

Stay safe tonight

For Everyone

  • Turn on two-factor authentication — email and banking first.
  • Use a password manager; never reuse a password.
  • Check old accounts against known data breaches and change anything reused.
  • Update phones and browsers — patches close doors attackers already know.

For Businesses

  • Audit before launch, not after the first incident.
  • Remove or protect staging servers and test admin panels.
  • Train staff on phishing — the inbox is the perimeter now.
  • Keep backups offline-tested; hope is not a recovery plan.
05 // Watch the Session

The interview, on YouTube

চলতি published the session as a three-part video series on their YouTube channel. Press play to watch right here — videos load only when you tap them, so this page stays fast.

সব জায়গায় ট্র্যাপ! বাঁচবো কীভাবে? — চলতি interview with Foysal Mahmud চলতি · YouTube
Video 02 · চলতি

সব জায়গায় ট্র্যাপ! বাঁচবো কীভাবে?

Traps are everywhere — phishing, fake offers and social engineering — and this is how you avoid them.

Open on YouTube
হ্যাকিং থেকে সতর্কতা! — চলতি interview with Foysal Mahmud চলতি · YouTube
Video 03 · চলতি

হ্যাকিং থেকে সতর্কতা!

Beware of hacking — how accounts actually get taken over, and the habits that keep yours yours.

Open on YouTube

ALSO ON FACEBOOK — the session was published there in two parts: Part 1 · Part 2

06 // The Guest

About Foysal Mahmud

Foysal Mahmud — Ethical Hacker

Foysal Mahmud

Ethical Hacker · Cyber Security Specialist · Dhaka, Bangladesh

Offensive security with a defensive conscience. Foysal Mahmud is hired to think like the adversary — probing web applications, networks and human-facing systems for the weaknesses others miss — then helps close them properly, permanently, and with evidence. Alongside client work, he speaks on national platforms about cybersecurity awareness, and builds secure software by design.

3+Years in Field
50+Clients Secured
180+Vulns Found
07 // Questions

Quick answers

Is ethical hacking legal?

Yes — when it is authorized. Ethical hackers work under a signed scope from the system owner. Testing a system you do not own or have written permission for is illegal, regardless of intention.

What does an ethical hacker deliver to a client?

A risk-rated report: each finding with proof-of-concept evidence, its business impact, and a remediation roadmap — followed by a re-test once fixes are in place.

How can I start learning cybersecurity?

Start with Linux, networking fundamentals and one scripting language (Python). Practice only in authorized labs, document everything, and build methodology before collecting tools.

Can Foysal Mahmud audit my website or business?

Yes — engagements are available for web applications, APIs, networks and security consulting. Use the contact section of the main portfolio; response time is under 24 hours.

Your system, tested first

The interview explains the philosophy. An engagement applies it to your website, app or network — before someone with worse intentions finds the same doors.

Start an Engagement See Field Records